Why ERP Security Matters More Than Ever for Business Continuity
Why ERP Security Matters More Than Ever for Business Continuity
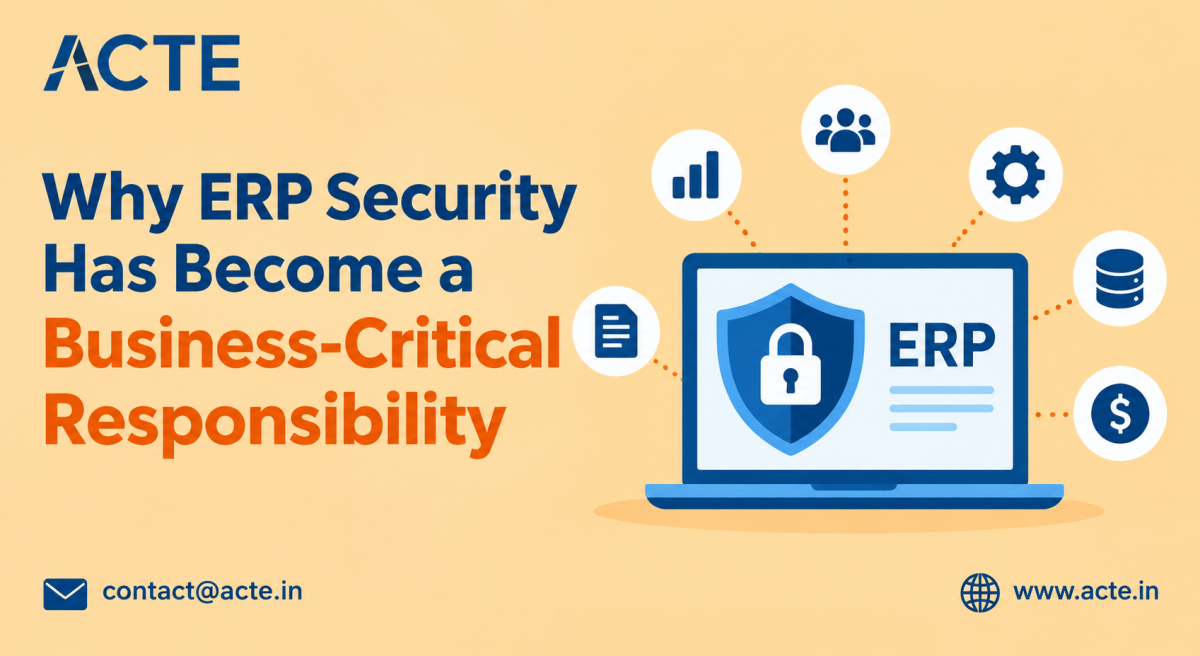
Enterprise Resource Planning (ERP) systems have become essential for organizations that want to manage their business processes through connected digital platforms. ERP applications can support finance, accounting, procurement, human resources, inventory, sales, manufacturing, and SAP Security GRC Course in Chennai supply chain activities. As these systems become more deeply integrated into daily operations, their security becomes increasingly important. Protecting ERP systems is now a business responsibility because security problems can affect information, productivity, compliance, and operational continuity.
ERP Systems Manage Business-Critical Data
ERP platforms bring large amounts of organizational information into a centralized environment. They may contain financial transactions, employee information, customer records, supplier details, purchasing information, inventory data, and management reports. Unauthorized access or changes to this information can create operational and financial problems. Organizations must therefore establish appropriate controls to protect data and ensure that business information remains accurate and accessible to authorized users.
Cyber Threats Require Greater Protection
Cybersecurity threats can affect ERP environments through several channels. Phishing attacks may compromise employee credentials, while malware and ransomware can disrupt systems and access important information. Weak passwords, outdated software, excessive permissions, and insecure integrations can also increase exposure. Businesses need proactive security practices that include vulnerability management, system updates, monitoring, and timely response to suspicious activities.
ERP Disruptions Can Affect Multiple Functions
ERP systems often connect several departments, meaning that a problem in one platform can have broader consequences. Finance may depend on ERP applications for accounting activities, while procurement uses them for purchasing and supplier management. Inventory, manufacturing, sales, and HR processes may also rely on the same environment. An ERP security incident can therefore interrupt several workflows at once, making system availability an important business consideration.
Access Control Reduces Unauthorized Activity
Managing user permissions is a fundamental part of ERP protection. Employees should receive access that matches their responsibilities, while sensitive functions should have additional safeguards. Role-based access controls can limit unnecessary privileges, and multi-factor authentication can provide SAP Security GRC Course in Bangalore stronger protection for accounts. Regular access reviews can also identify accounts or permissions that are no longer appropriate.

Security Supports Compliance and Governance
Businesses may be required to protect certain information because of regulations, industry standards, contractual obligations, or internal policies. ERP security controls can help organizations meet these requirements by providing better SAP Security GRC Course in Hyderabad control over access and information handling. Audit logs, documented procedures, monitoring systems, and periodic reviews can improve transparency and help organizations identify potential weaknesses.
Employees Influence Security Outcomes
Employees are an important part of ERP security because they interact with systems and information every day. Human mistakes can create opportunities for attackers or lead to accidental data exposure. Training employees to identify phishing attempts, protect credentials, follow security procedures, and report unusual activity can reduce these risks. Security awareness should be treated as an ongoing organizational practice rather than a one-time training exercise.
ERP Security Requires Ongoing Management
Protecting an ERP environment requires continuous attention. Organizations should regularly review permissions, install security updates, monitor user activity, test backups, assess vulnerabilities, and maintain incident SAP Security GRC Online Course response procedures. Security should also be considered whenever new ERP modules, third-party applications, integrations, or cloud services are introduced. Regular reviews help organizations adapt their security controls as business requirements change.
Conclusion
ERP security has become a business-critical responsibility because these systems support essential operations and manage valuable organizational information. A security incident can affect several departments and potentially disrupt normal business activities. By implementing strong access controls, improving employee awareness, monitoring systems, assessing vulnerabilities, and maintaining effective recovery procedures, organizations can strengthen ERP security and create a more resilient business environment.
Comments (0)